#infosec

3513 posts · Last used 10h

Boosted by @fedicat@pc.cafe
Freeradical.zone is a Mastodon server themed around infosec and privacy and technology and leftward politics and cats and dogs. This server has been online since 2017. :Fediverse: https://freeradical.zone You can find out more at https://freeradical.zone/about or contact the admin account @tek@freeradical.zone#FeaturedServer #InfoSec #Privacy #Tech #Mastodon #Fediverse #FreeFediverse
1
0
1
0
Microsoft openly admitting they have not(!) had MFA, network segmentation, least privilege, software lifecycle, jump-servers, asset- and software-inventory etc for Azure PROD for years and they are not there yet. This whole report is just so scary. At the same time, good that they are finally working on it and making it transparent. Source: https://cdn-dynmedia-1.microsoft.com/is/content/microsoftcorp/microsoft/final/en-us/microsoft-brand/documents/sfi-april-2025-progress-report.pdf #Microsoft #azure #infosec
220
1
200
0
RE: https://infosec.exchange/@ifin/117630530054379148 I am firmly of the opinion that for almost all the websites using CDNs, they are basically of no benefit and are used only due to cargo-culting from the olden days when browser cache was not compartmentalized between origins and HTTP/2 did not exist. For years I've been saying CDNs are a net liability for most websites; one of the reasons is that they are a juicy target. Anyone with sufficient access gets to deploy any JS to any site that pulls JS from them. Lo and behold… #WebDev #InfoSec
Quoting
It's late, but we wanted to get this story out. 186 popular sites were compromised today with malicious JavaScript. The injected code could skim card numbers, steal cryptocurrency, take screenshots, and even deliver iOS malware. https://ifin.network/t/optimizely-cdn-compromised-to-steal-cards-crypto-deliver-malware/994 #ThreatIntel
Open quoted post
99
0
84
0
Claude Code has been storing developer passwords in plain text files, which in some cases have ended up on Github. Anthropic: Our large language models are the future of infosec! Also Anthropic: Claude Code's "don't ask again" feature saved passwords, API keys and SSH logins in plain text to .claude/settings.local.json files exposed across more than 1000 public GitHub repositories. By @juha@mastodon.nz / @juha.bsky.social at IT News: https://www.itnews.com.au/news/dont-ask-again-in-anthropics-claude-code-leaks-developer-secrets-630203 @fuck_ai #infosec #cybersecurity
82
1
87
0
Nearly 25 years ago, I worked in the IT Security field. Well, it was called InfoSec back then (yes, I'm old). I left the field because of a terrible boss who, as I found out later, was fired. In one day, 5 of my co-workers left with me. I was never able to get back into the field. That's sad. But following so many awesome IT Security/CyberSecurity folks here in the Fediverse keeps me up to date on what's going on out there in the field that I once loved working in. I love the stories, journalism, research, podcasts...All of it. The Fediverse really is a great place. #infosec #cybersecurity
12
1
3
0
Bonjour le Fediverse 👋 Le Lab Technique est un site francophone de cybersécurité pour les PME et les curieux : 🍯 ce que voient nos pièges à attaquants (vrais robots, vrais chiffres) 🕵️ veille dark web et rançongiciels 🛠️ guides homelab et outils gratuits Chaque nouvel article arrive ici automatiquement. Les réponses à vos messages, elles, sont écrites par un humain. https://lelabtechnique.fr/?utm_source=mastodon&utm_medium=social #introduction #cybersécurité #infosec #homelab #darkweb
0
0
1
0
Hello, infosec.exchange. We are NSS Research, the research team behind NSS (Nexus Sentinel Station). We publish technical papers on phishing kits, look-alike domains, malicious apps and the hosting behind them. Each one is TLP:CLEAR, says how we know what it claims and where that stops, and comes with its full indicator list. Papers: https://nsshq.com/research?from=mastodon Indicators: https://github.com/nsshq/nssresearch Corrections and questions welcome, here or at hello@nsshq.com. #introduction #ThreatIntel #infosec
0
0
1
0
Hello, fediverse 👋 This account posts every PHP, Composer and WordPress vulnerability that gets added to CISA's Known Exploited Vulnerabilities list: what's affected, the fixed version, and a link to the advisory. It's the short list that matters: today 36 of about 19,500 PHP vulnerabilities are known to be exploited. Posts are automatic. I'm Oroma, I build phpwarden (an open-source PHP vulnerability scanner) and I read the replies. #PHP #WordPress #infosec #introduction
1
0
2
0
If you use #Telegram or know someone who does – there seems to be a remote code execution vulnerability in Telegram: https://nitter.catsarch.com/v12sec/status/2120471754166415821 It is apparently being actively exploited. The vulnerability is *bad*, it can lead to account take over or worse as it apparently provides the attacker with a way to run code directly on the device, outside of the sandbox. Apparently it has now been patched, so install updates as soon as possible! It relates to the new "widgets". #InfoSec
11
0
31
0
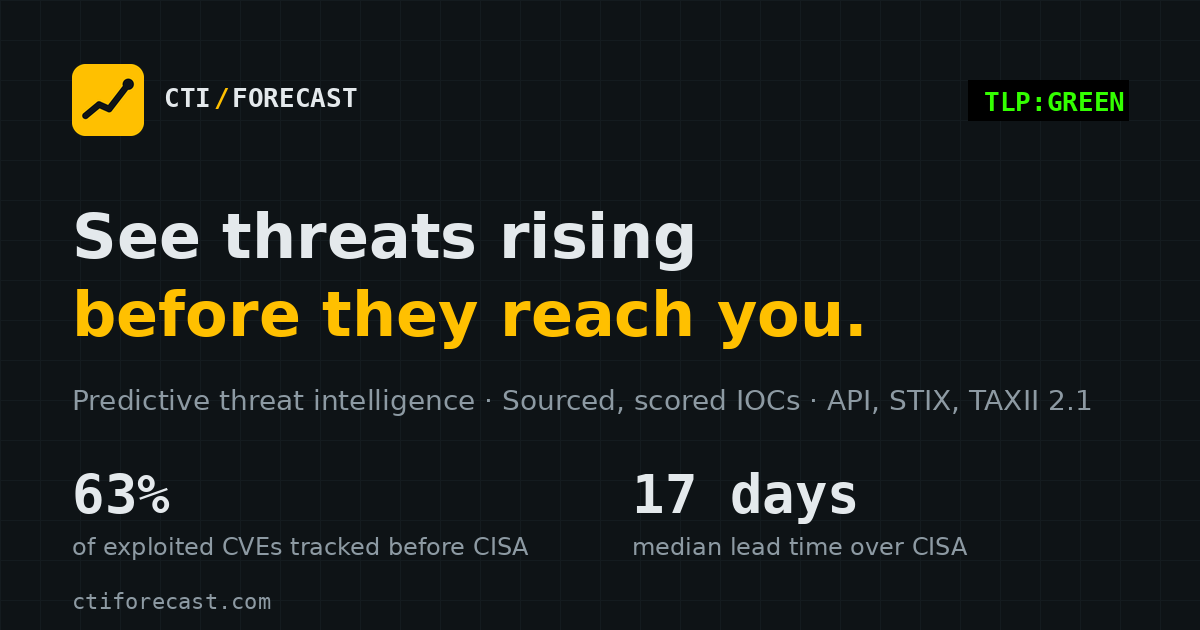
Hi Fediverse 👋 We're CTI Forecast, an independent threat intel project from Lyon, France. What we do: • Scored IOC feeds (IPs, domains, hashes) over STIX/TAXII 2.1 • CVE exploitation forecasts, before CISA KEV listing • Our own honeypots: attackers who break in get reported to AbuseIPDB & shared on OTX Free public blocklists: https://ctiforecast.com/en/ #introduction #threatintel #infosec #CTI #honeypot #blueteam
0
0
1
0
NBC News reports that some top US cybersecurity firms are turning away new customers seeking emergency help as AI-aided attacks surge. Sophos, which sells incident response services, says other DFIR firms have asked it for overflow support when their teams reach capacity. Sophos's advice is to have a tested plan before you need outside help. https://www.sophos.com/en-us/blog/why-incident-response-demand-will-grow-faster-than-expected #DFIR #InfoSec
10
0
13
0

Security / privacy heads up: It looks like Google is now publicly linking the phone number on Google Pixel phones (or at least Pixel 6 and up) to any Gmail/Google account you've logged into that phone with.

"Phone number verification is turned on by default. We verify the phone number and add them to all Google Accounts that are signed in on the device. This applies to both current and future accounts and phone numbers. "

I.e., if you write erotica, have an Only Fans, do sex work, etc., and you have logged into your alt email addresses on your phone, Google will now make your personal phone number "findable" for anyone who has that email address.

This will potentially adversely affect a lot of (vulnerable and/or marginalized) people.

Everyone has been opted into this by default (because who has heard of consent or security in tech circles grrr).

To opt out:

  1. On your phone, go to Settings, then next to your account name at the very top, go to "Google Services and Preferences".

  2. Under “Privacy & security,” select Phone number verification.

  3. Select whether to verify your phone number.

If you don't want your different identities linked and findable, make this change asap.

I hope that tech and especially infosec people and privacy advocates raise hell about this. (No one listens to the rest of us.)

*I don't work in tech, but I haven't seen tech people talk about this yet (from my limited Fedi vantage point).

Stay safe and keep your people safe.

Read more in the Google support pages.

https://support.google.com/android/answer/7521240

You're welcome to boost or share this post, but if you see tech professionasl discuss it, I'd much rather you quote them, and if you discuss this outside of Fedi, please do not give me credit. I don't need reply guys coming at me, I just want to flag people on what might be a problem. Thanks for your understanding.

#Infosec #Cybersecurity #Google #Pixel #Gmail
114
0
205
0